AI is the new Trojan Horse, and Bangladesh's gates are wide open
Bangladesh runs its offices, banks and homes on software that cannot be updated and was never paid for. Artificial intelligence has just made attacking it a job almost anyone can do.
AI is the new Trojan Horse, and Bangladesh's gates are wide open
Bangladesh runs its offices, banks and homes on software that cannot be updated and was never paid for. Artificial intelligence has just made attacking it a job almost anyone can do.
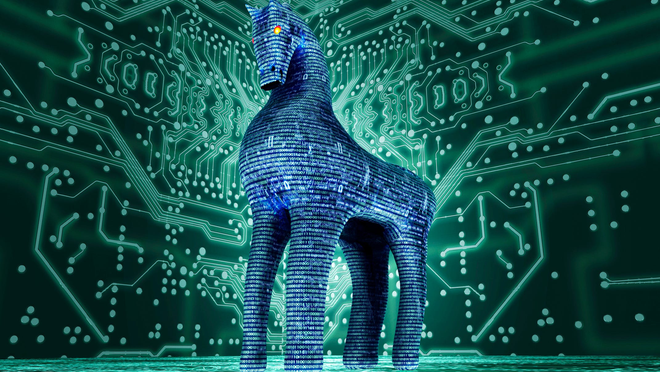
Two thousand years ago, Virgil gave the world its most durable lesson in security. Troy had held its walls for ten years. What undid the city was not a stronger army but a gift the Trojans carried through the gates themselves. One man, the priest Laocoön, warned them: I fear the Greeks, even when they bring gifts. Nobody listened, because the horse looked like a prize and everyone was tired of being careful.
The internet learned the same lesson in a single week. On 4 May 2000, an email began arriving in inboxes around the world with the subject line ILOVEYOU and an attachment that appeared to be a love letter.
It was a small script written by Onel de Guzman, a 23-year-old college dropout in Manila who could not afford dial-up internet and wanted to steal other people’s passwords to get online. When a recipient opened the letter, it mailed itself to everyone in their address book. Within days it had infected roughly one in ten computers connected to the internet. The House of Commons shut down its servers.
The Pentagon and the CIA scrambled to contain it. The damage was later put at about ten billion dollars. The Philippines had no law under which to charge him, so he was never tried. He was found two decades later running a phone repair stall in a Manila shopping centre. ILOVEYOU could not choose its victims. It spread wherever an address book carried it, indifferent to who opened the file. An agentic system has no such limit. It can be told a company’s name, a bank’s domain, a target’s job title, and it will adjust its approach for each one, patiently, without losing interest or making the same mistake twice.
The affair frightened the world because of what it revealed about the ratio of effort to harm. One young man with a cheap computer and a few hundred lines of code had disrupted governments on three continents. For the next twenty-five years, the cyber security industry consoled itself that this was still rare: serious attacks needed serious skill, and serious skill was scarce. That consolation has just expired.
In November last year, the AI company Anthropic disclosed that a group it linked to the Chinese state had used its Claude Code tool to run an espionage campaign against roughly 30 organisations, among them technology firms, banks, chemical manufacturers and government agencies. The attackers persuaded the system that it was working for a legitimate security firm doing authorised testing. Once inside, the AI did the reconnaissance, found the weaknesses, wrote the exploit code, harvested passwords and pulled out data. By the company’s own estimate, it carried out 80 to 90 per cent of the operation on its own. Human beings intervened at a handful of decision points, for perhaps twenty minutes in total. The thirty organisations in that campaign were not soft targets. They were firms with security teams, patched systems and budgets built for exactly this threat, and the AI still did most of the work. Point the same tool at a target with none of those defences, and the arithmetic stops being frightening and starts being obvious.
De Guzman at least had to write his own code. The attackers of 2025 mostly had to describe what they wanted. Everything that once separated a serious intruder from an ambitious amateur, the patience, the technical knowledge, the hours of trial and error, has been packaged and is available for a monthly subscription. This is what “agentic” AI means in practice: not a chatbot that answers questions, but software that browses, clicks, writes code and runs tasks for hours without supervision. The same tools that will let a small Chittagong exporter automate its paperwork will let a teenager in another country automate a burglary. And because such an agent can try a thousand doors in the time a human tries one, it will find the ones nobody bothered to lock.
Now consider what such an agent would find if it were pointed at Bangladesh.
It would find the most unprotected computing environment in Asia. The software industry’s last global survey put the share of unlicensed software in Bangladesh at 84 per cent, the highest in the region. A pirated copy of Windows cannot safely receive security updates, so every flaw discovered since it was installed stays open. Paid antivirus is treated as a luxury. In 2022, Kaspersky’s data placed Bangladesh first in the world for the share of users hit by Trojan attacks. The following year, a security researcher in Europe found the names, phone numbers and national ID numbers of some 50 million Bangladeshis sitting on a government website, reachable through an ordinary Google search.
It would also find a financial system that has moved online faster than its defences. Bangladesh Bank recorded 81,423 cases of fraud in 2025, costing customers Tk926 million. Eighty-eight per cent of the money was taken through mobile financial services, and less than 9 per cent of it was ever recovered. Most of that fraud still depends on a human voice on the phone and a message written in shaky Bangla. Generative AI removes both tells. It writes fluent, polite, locally idiomatic Bangla. It clones a voice from a few seconds of a Facebook video.
Much of today’s mobile money fraud already runs on a caller posing as customer service, asking a victim to read out an OTP or confirm a PIN. That scam succeeds only when the voice sounds plausible enough to be believed for the length of one phone call. AI does not invent a new fraud; it simply removes the one weakness the old version depended on. The scam that used to fail because it sounded wrong will now sound like your bank manager, or your son. Fraud is a numbers game, and AI has just changed the numbers: a caller who once needed an hour per victim can now run hundreds of conversations at once, each one patient, fluent and tailored to the person on the other end.
There is a further harm that does not appear in any cyber security framework but grows from the same soil. Police Cyber Support for Women, the unit the police set up in 2020, received requests for help from more than 60,000 women in its first four and a half years, and more than 9,000 in 2024 alone.
Two in five complaints concerned the publication of private information; others involved hacked accounts, blackmail and impersonation. Cyberbullying is not a network intrusion. But it is what happens when millions of people are handed a smartphone and no protection, no training and little expectation of redress, and AI tools that fabricate intimate images in seconds are about to make it much worse. Any serious national conversation about digital safety has to hold both problems in the same hand.
Why is the base so weak? Not because Bangladeshis are careless. A licensed office suite costs more than many small firms earn in a week, so piracy became the default and updating became a habit nobody formed. Companies keep a single overworked IT person, if that, and treat security as a cost to be deferred until something breaks. Victims rarely report, because they expect nothing to come of it, and so the true scale of the problem is never measured. And the country produces too few defenders: the skills that AI now hands to attackers for free remain expensive and scarce on the defending side.
Bangladesh is not alone in facing this, and it is not starting from zero as a matter of policy. India’s CERT-In has spent a decade building mandatory breach-reporting and incident-response rules that Bangladesh’s own framework closely resembles in ambition, if not yet in enforcement. Sri Lanka passed a dedicated Cyber Security Act in 2024 after its own run of high-profile breaches. The lesson from both is not that Bangladesh is behind some unreachable standard, but that the standard is reachable, and other governments in the region have already shown what enforcing it looks like.
None of this is hopeless, and it is worth saying that the direction of policy is right. Bangladesh Bank’s 2026 cyber security framework, which requires banks, mobile money operators and payment firms to adopt multi-factor authentication, real-time monitoring and proper incident response by the end of this year, is a sound document. The task now is to make it bite, and to extend the same seriousness beyond the banks.
Four steps would matter most.
First, legalise the base layer. The government could negotiate national licences for the software its offices and schools actually use, or commit in earnest to open-source alternatives that receive updates for free. Either is cheaper than another data leak. An unpatched machine in a land office is not a private matter; it is a door into the state.
Second, slow the money down. Mobile financial services should introduce a short delay and a second confirmation on large or unusual transfers, particularly for older customers, and should be judged publicly on their recovery rates. Under 9 per cent is not acceptable when the operators hold the data to do better.
Third, publish a one-page Bangla baseline for small businesses and families, and repeat it until it is as familiar as a road safety slogan: update your software, turn on two-step verification, never act on a voice alone, call back on a number you already have. The National Cyber Security Agency is well placed to lead this, and television and mosque committees, not just Facebook, should carry it.
Fourth, build the defenders. Every AI capability that helps an attacker helps a defender who knows how to use it. Universities should be funded to train people in exactly that, banks and telecom operators should be pushed to hire them, and the police units that deal with fraud and harassment should be given the tools and the staff their caseloads demand. A country that exports software engineers can surely keep a few hundred of them guarding its own doors.
Laocoön’s warning was not against gifts. It was against accepting them without looking inside. Bangladesh has spent twenty years carrying unexamined software through its gates because it was free and the walls seemed to hold. The horse still looks like a gift. The difference now is that it builds itself, and it does not get tired.
This article is co-authored by S M Mashrur Arafin Ayon, a Research Associate at SIPG, North South University, and Mursalin Haque, an undergraduate student at North South University.